NIST SP 800-53
Use federal standards to secure your organization
Evolve your security and privacy program
The NIST SP 800-53 framework is mandatory for federal systems of the United States and is often adapted and applied by private organizations. Because NIST SP 800-53 requires many controls, knowing where to start can be daunting. Our consultants have deep experience with NIST 800-53 and can help scope, design, implement, document, and assess your NIST SP 800-53 program. From scoping to reviewing, TrustedSec can help organizations at any point in their compliance journey.
- Scope - Set your program up for success by ensuring proper scoping and baselines for your information assets and systems.
- Implement - Design and tailor your program to ensure applicability and effectiveness.
- Document - Build all of the documents you'll need to run and attest to your security program.
- Review - Assess the effectiveness of your security program by identifying all barriers to full compliance. Recommendations detail ways to meet the intent of identified gaps.
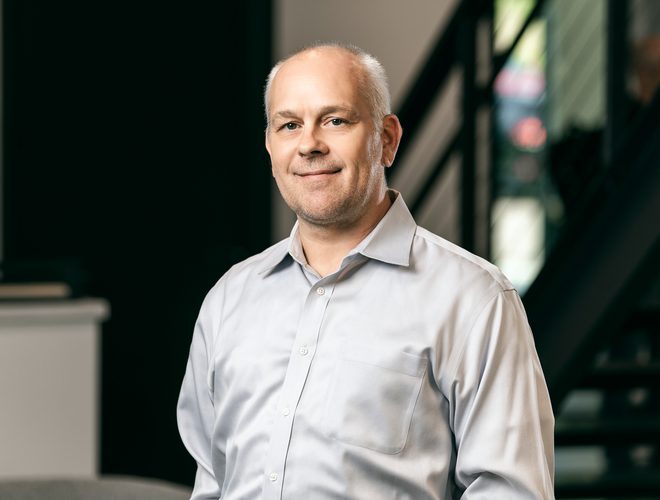
“Weaving risk, group theory, and adaptation with business strategy is one way we stand out.”Rockie BrockwayDirector of Advisory Innovations
Rockie Brockway
Director of Advisory InnovationsRockie's focus is on helping organizations strengthen their security posture by better aligning security with business needs and requirements.
Empower your business through better security design.
Talk directly with our experienced advisory consultants to learn how we can help.
Read our blog
Explore trending cybersecurity topics on the TrustedSec Security Blog
The Quiet Phase: Why Active Directory Group Enumeration Deserves Your Attention
Most teams watch the door; the window gets less attention. In this blog, we cover how auditing Active Directory group enumeration surfaces attacker…

What is CUI? A Contractor’s Perspective
Three questions every government contractor should be able to answer about CUI—how to identify it, when to mark it, and how to handle it correctly. In this…
Trimarc, 18 Months Later at TrustedSec
Eighteen months after Trimarc joined TrustedSec, the work speaks for itself. In this blog, we reflect on Trimarc’s integration into TrustedSec and what it…
Handling Pre-Contract FCI and CUI
CMMC requirements don’t exist before a contract does and that distinction matters. In this blog, we clarify what FCI and CUI obligations apply during the…

Two Config Files, Two Release Tracks, and One Very Bad Commit
Some of the best infrastructure improvements start with one bad afternoon. In the final part of this blog series, we walk through the configuration, release…
TrustedSec Joins the OpenAI Daybreak Defense Network
We're part of OpenAI’s Daybreak Defense Network—what does that mean for our customers? Go deeper, get to the evidence faster, and make real security…
Logging is a Discipline, Not a Switch
Logging isn't a switch to flip; it's something to tune and maintain. In this blog, we outline a four-step Active Directory logging framework covering log…
HashcatRosetta: Reading the Rosetta Stone of Password Cracking
Meet HashcatRosetta—the Hashcat rule decoder you didn't know you needed. In Part 2 of this blog series, we go through how it translates, analyzes, and…

What's New in hate_crack Since 2.0
You thought you knew hate_crack 👀 Well, version 2.0 changed that. In Part 1 of this latest blog series, we go through 13 new attack methods, menu…
Unpacking a laZzzy Donut
Six stages. Multiple encryption layers. One static analysis. In this blog, we unpack a multi-stage malware loader combining Python obfuscation, Donut…